


Embedded Hardware Acquisition & Analysis Training - Teel Technologies
Embedded Hardware Acquisition & Analysis Training will focus on processes and methodology that examiners can use to access digital data at the logical and physical levels from: IoT devices, Smart TVs, Vehicle Modules, Skimmers/Shimmers, Routers and almost every device that utilizes a main board, controller chip and some forms of flash memory. New content includes accessing, decoding and circumventing security methods and encryption keys using reverse engineering and power glitching techniques.
Description
Students will be provided with a foundation of how electronics work in relation to the techniques being used in this training. The processes taught will include tools from cost effective sources, open source resources, and commercial tools.
Students will learn how to adapt techniques like ISP, Chip-Off, Reverse Engineering and Voltage Glitching and apply it to embedded devices commonly using communication protocols such as SWD, SPI, i2C, UART and more, to exploit components and recover and decode data from various sources like embedded code and the flash memory of controller chips. Data from these sources can then be analyzed for evidence or malware artifacts.
Prerequisites
This course is open to all digital forensic professionals.
Due to the sensitive nature of our curriculum, and industry, all potential students are subject to vetting prior to enrollment. We reserve the right to refuse registration to any person that does not meet our established criteria.
Laptop Requirements
- Windows PC with two (2) USB A ports.
- Windows OS
- macOS with Bootcamp Windows
- macOS alone will not work (No Virtual Machines)
- 8GB RAM (minimum)
- 100GB storage (minimum)
- You must have admin rights or have the admin password for software installation.
- NOTE: ALL Windows updates should be done prior to class.
Course Itinerary
Abbreviated. Contact us for complete syllabus.
Day 1 Overview
- Introduction
- Advanced Hardware Forensics
- Digital Communications
- Logic Analyzer Setup and measure
- Electronics Theory
Day 2 Overview
- Multimeter Basics
- Validation Ruler
- Bluetooth
- SPI & i2C
- Reverse Engineering Electronic Device
Day 3 Overview
- PuTTY
- SPI Walkthrough
- Chip Programmer Walkthrough
- Researching Hardware
- Reverse Engineering
- Processors
- Encryption
Day 4 Overview
- Assembly Language
- SWD Protocol
- Various SWD Debuggers/Programmers
- Demonstration – Bypass Encryption
- Lab 2 – Bypass Encryption
- Ghidra
- OpenOCD & GDB
- Lab 3 – Bypass Encryption
- Lab 4 – Bypass Encryption
Day 5 Overview
- CMD42 Sniffing
- Linux User Passwords
- Routers
- Hands-On Router Access
- Routers - Decrypted Files - Instructor Walkthrough
- Glitching Techniques
- Crowbar Glitching Lab
Included with Training
All students receive a certificate of completion.
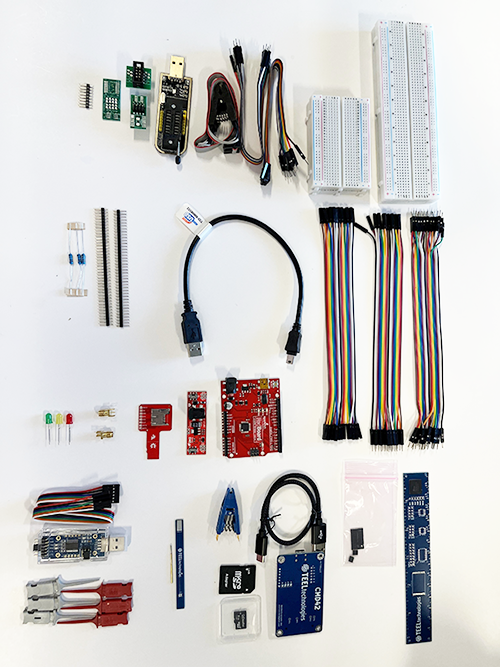
Each student receives the new Teel Tech EHAAT toolkit that includes tools used in class, as well as the Teel Tech CMD42 utility for identifying locked monolith memory (SD, microSD, etc.), validation ruler and Micro Sniffer.
Teel Tech EHAAT toolkit contents include:
- CH341A Programmer (1)
- Sparkfun Red Board - Arduino (1)
- USB to USB Mini Data and Power Cable (1)
- SMA Connector x1 (1)
- EHAAT CMD42 Board (1)
- EHAAT MicroSD Card Sniffer 2.0 (1)
- USB to TTL (1)
- EHAAT Probe (2)
- Pomona SOIC8 Clip (1)
- Grabbers with Wire Port, 3 red, 3 grey (6)
- Bread Board, 2 small and 2 large (4)
- Jumpers, 10 each of male, female, and male to female (30)
- LED Emitting Diode 5mm, 3 different colors (3)
